Improved security on sign-in types
As requested by some of you we have improved the security settings around allowed/disallowed sign-in types on your organization. In case you forgot, the security settings previously offered you to enforce two-factor authentication on users with username/password and disallow users from all social providers only. With the improved settings, you can pick exactly which sign-in type you want to allow accessing your organization:
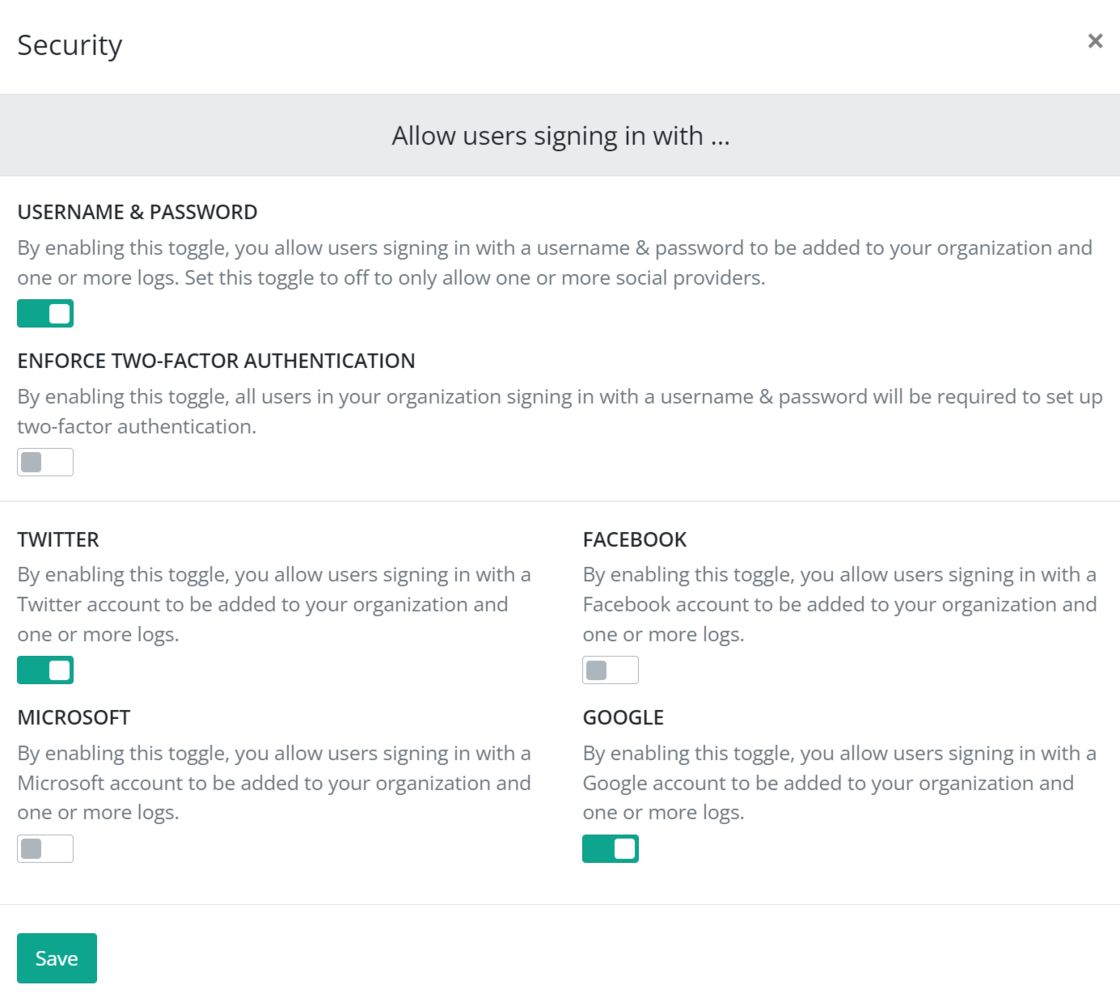
By default, all sign-in types are allowed on new organizations. For existing organizations, we have migrated your existing security settings to the new model.
If you want to learn more about the new security settings, check out the updated documentation.